Every Archived URL.
Ranked for Recon, Built for Speed.
Stream millions of Wayback Machine captures directly into an interactive triage workspace. Uncover hidden endpoints, leaked credentials, forgotten subdomains, and live assets without drowning in raw text dumps.
git clone https://github.com/pratik-khairnar-sec/wayback-lens.git
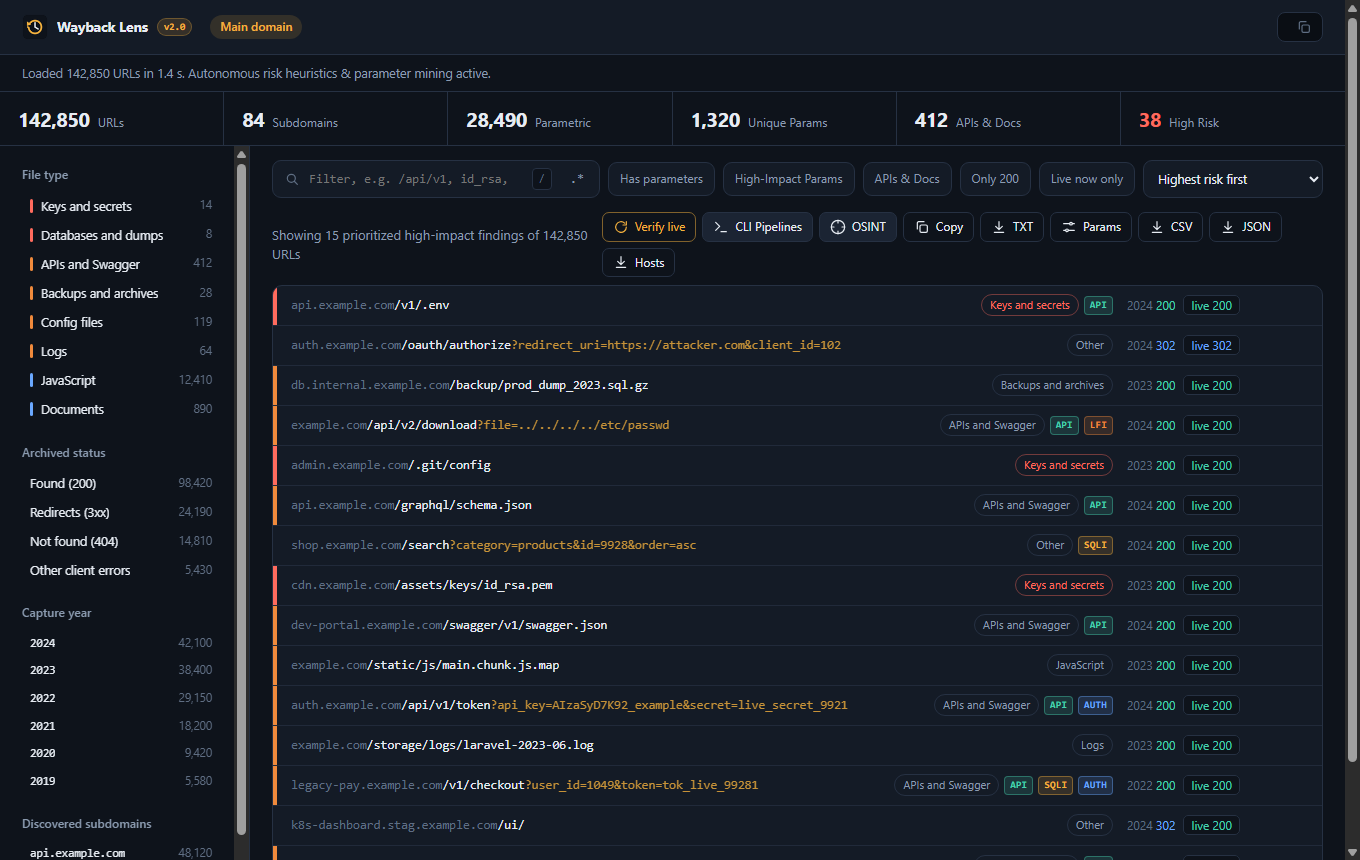
Interactive Recon Simulator
Test the heuristic triage engine right here. Click a scan profile and filter findings live.
Targeted Scan Modes
Six targeted recon scopes designed to extract exactly what matters for your engagement.
Main Domain (Host Scope)
Every archived URL on the exact hostname. url=host/*
All Subdomains
Passive subdomain enumeration covering the root host and all subdomains. matchType=domain
Sensitive Files
Backups (.bak, .sql), private keys, .env, configs, logs, and dumps.
JavaScript Bundles
Archived .js and .mjs files to uncover hidden API endpoints and leaked keys.
APIs & Swagger
REST endpoints, GraphQL, Swagger schemas, and OpenAPI specs for API hunting.
With Parameters
Query-string endpoints ready to feed into fuzzers for SSRF, SQLi, and IDOR testing.
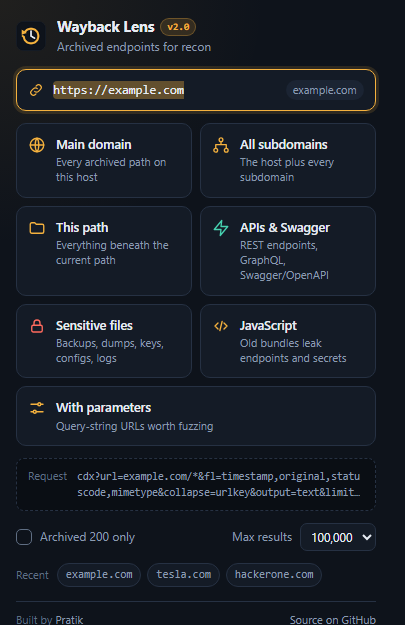
Extension Popup: pre-fills active tab, previewing live CDX query.
Engineered for High-Velocity Recon
Built from scratch to overcome the slow, clunky, and memory-heavy limitations of legacy archive extractors.
Non-Blocking Stream Processing
Uses chunked ReadableStream parsing to ingest and display 100,000+ CDX records without lagging your browser or eating gigabytes of RAM.
Heuristic Risk Scoring
Pre-filters noise and surfaces high-value targets first: .env files, AWS tokens, SQL database dumps, .git directories, and backup archives.
Live HEAD Verification
Multi-worker prober checks which historical URLs actually respond with HTTP 200 today, helping you find active vulnerable endpoints instantly.
Instant Regex & Faceted Filters
Filter on-the-fly by HTTP status code, target subdomain, query parameters, or arbitrary Regular Expressions with zero round-trip delay.
Universal Export Suite
Export your tailored triage view as clean TXT, CSV, JSON, or extract a deduplicated passive subdomain host list ready to pipe into subfinder or httpx.
Parameter Mining & Fuzzing Wordlists
Autonomously extracts all unique query parameters, classifying high-impact candidates for SSRF, LFI, SQLi, and auth bypass fuzzing with 1-click wordlist export.
Ready-to-Run CLI Pipelines & OSINT
Generate and copy instant terminal commands for Nuclei, FFuF, HTTPx, and SQLMap, plus 1-click pivots into Shodan, crt.sh, and URLScan.io.
100% Offline UI & Zero Telemetry
Zero third-party analytics, zero cloud dependencies, strict Manifest V3 CSP, and inline SVG assets. Captured URLs are sanitized and never executed.
How Wayback Lens Compares
Why security teams and bounty hunters choose a dedicated visual recon workspace.
| Feature | Wayback Lens | gau / waybackurls | Web Archive UI |
|---|---|---|---|
| Interactive Triage Workspace | ✓ Yes (Real-time) | ✗ CLI Text Dump | ✗ Static HTML |
| Autonomous Risk Scoring (.env, SQL, keys) | ✓ Heuristic Engine | ✗ Manual Grep | ✗ None |
| Live HTTP 200 Prober | ✓ Built-in Multi-Worker | ✗ Pipe to httpx | ✗ None |
| Subdomain Extraction | ✓ 1-Click Export | ✗ Custom Awk/Sed | ✗ None |
| Active Tab Target Detection | ✓ Auto Pre-fill | ✗ Manual CLI flag | ✗ Manual URL input |
| Streaming 100k+ URLs without Freezing | ✓ Stream Decoder | ✓ Fast stdout | ✗ Timeouts |
| Parameter Mining & Fuzzing Wordlists | ✓ 1-Click Params Export | ✗ Pipe to qsreplace | ✗ None |
| Terminal CLI Pipelines (Nuclei/ffuf/httpx) | ✓ Built-in Generator | ✗ Manual bash commands | ✗ None |
Quick Start Guide
Install in under 60 seconds on any Chromium-based browser (Chrome, Brave, Edge, Arc, Opera).
Clone or Download
Grab the official release ZIP or clone the repository:
git clone https://github.com/pratik-khairnar-sec/wayback-lens.git
Enable Developer Mode
Open chrome://extensions in your browser and switch on the Developer mode toggle in the top-right corner.
Load Unpacked
Click Load unpacked and select the project folder. Pin the extension icon to your toolbar for immediate access.
Responsible Reconnaissance & Scope Notice: While Wayback Machine archives represent public historical telemetry, probing active production endpoints with the Verify Live feature must only be conducted against targets within authorized bug bounty scope or under explicit penetration testing permission.